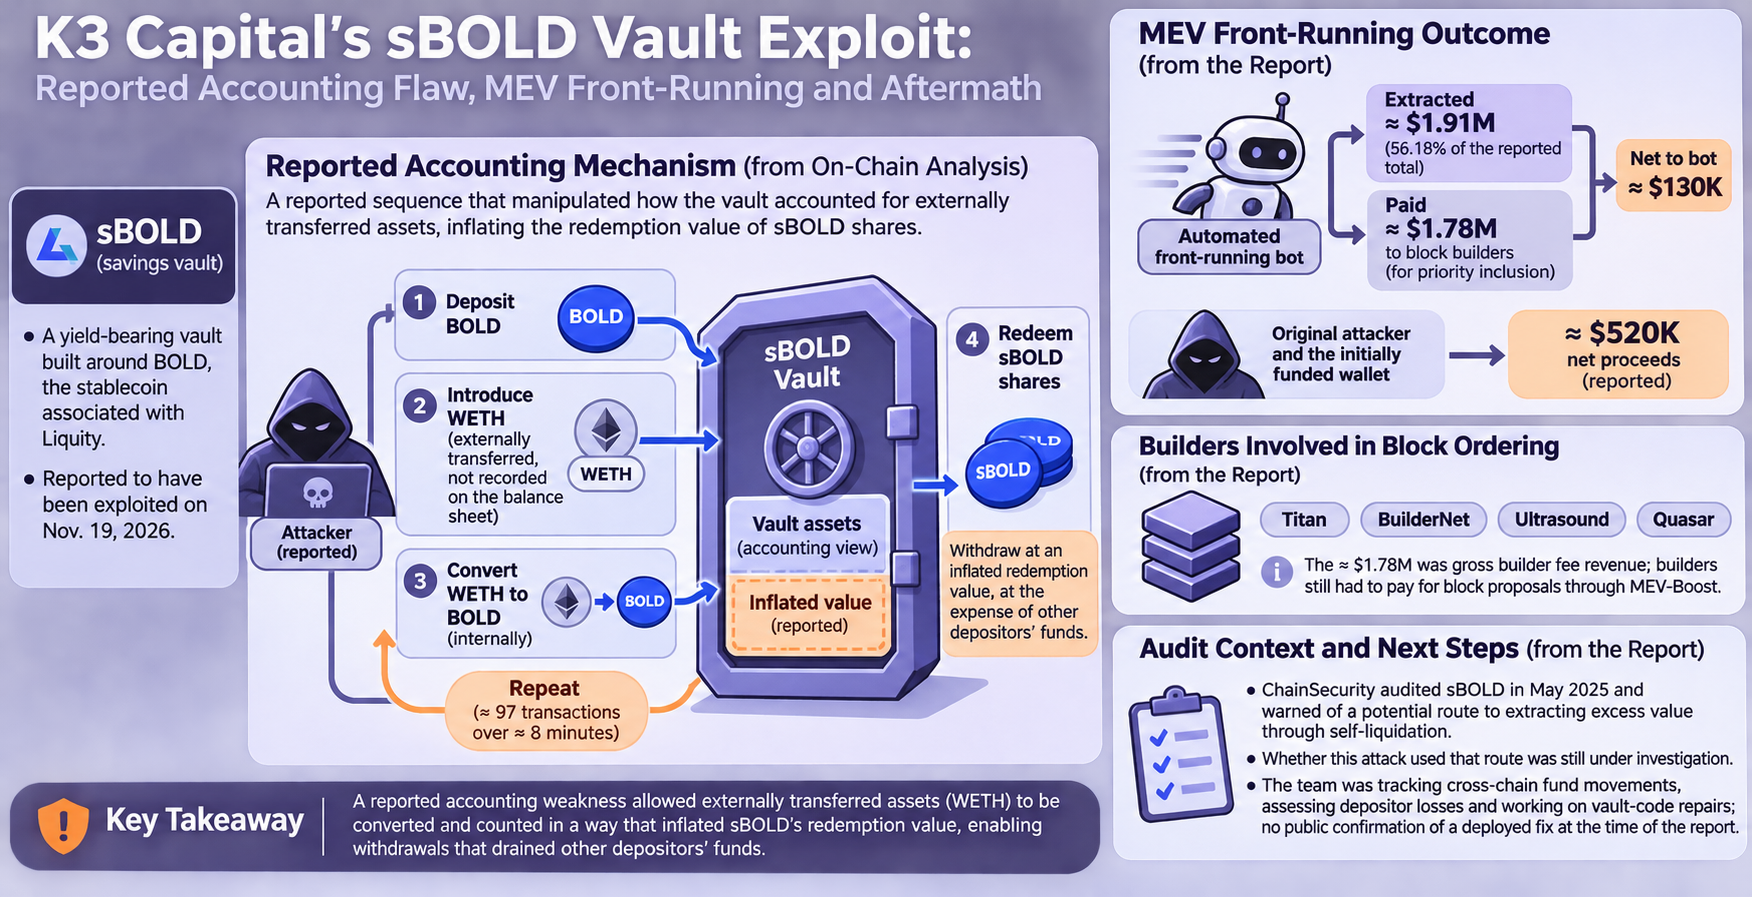
As reported on November 19, 2026, K3 Capital’s Ethereum-based sBOLD savings vault had been exploited for approximately $3.4 million. The reported attack involved 97 transactions over roughly eight minutes. sBOLD is a yield-bearing vault built around BOLD, the stablecoin associated with Liquity.
What happened to the vault’s share accounting?
According to Bitquery’s transaction analysis, the attacker exploited how the vault accounted for the value of externally transferred assets. The reported sequence involved depositing BOLD, introducing wrapped ether (WETH) that was not recorded on the balance sheet, and converting it internally to BOLD. Repeating those actions inflated the apparent redemption value of sBOLD shares, allowing withdrawals at the expense of other depositors’ funds. This is an account of the reported mechanism, not a tested procedure for reproducing it.
Where did the extracted funds go?
Bitquery reported that an automated front-running bot copied and modified the original attacker’s withdrawal transaction after detecting it in the mempool. The bot extracted approximately $1.91 million—56.18% of the reported $3.4 million total—but paid around $1.78 million to block builders for priority inclusion, leaving it roughly $130,000. The report says the original attacker and the wallet that initially funded the attack ultimately received approximately $520,000 in net proceeds.
The report names Titan, BuilderNet, Ultrasound and Quasar among builders involved in ordering related blocks. On-chain researchers cautioned that the $1.78 million was gross builder fee revenue: builders still had to pay for block proposals through MEV-Boost.
ChainSecurity audited sBOLD in May 2025 and warned of a potential route to extracting excess value through self-liquidation. Whether this attack used that route was still under investigation at the time of the report. The report also said the team was tracking cross-chain fund movements, assessing depositor losses and working on vault-code repairs; it did not establish that a fix had been deployed.