Originally reported November 11, 2026, at 20:49 UTC+8. Bitcoin Core publicly disclosed three security vulnerabilities the previous day. Fixes had already shipped in Bitcoin Core 30.0 on October 10, 2025, and 29.2 on October 14, 2025. The disclosures do not describe newly released patches.
Check your version and configuration
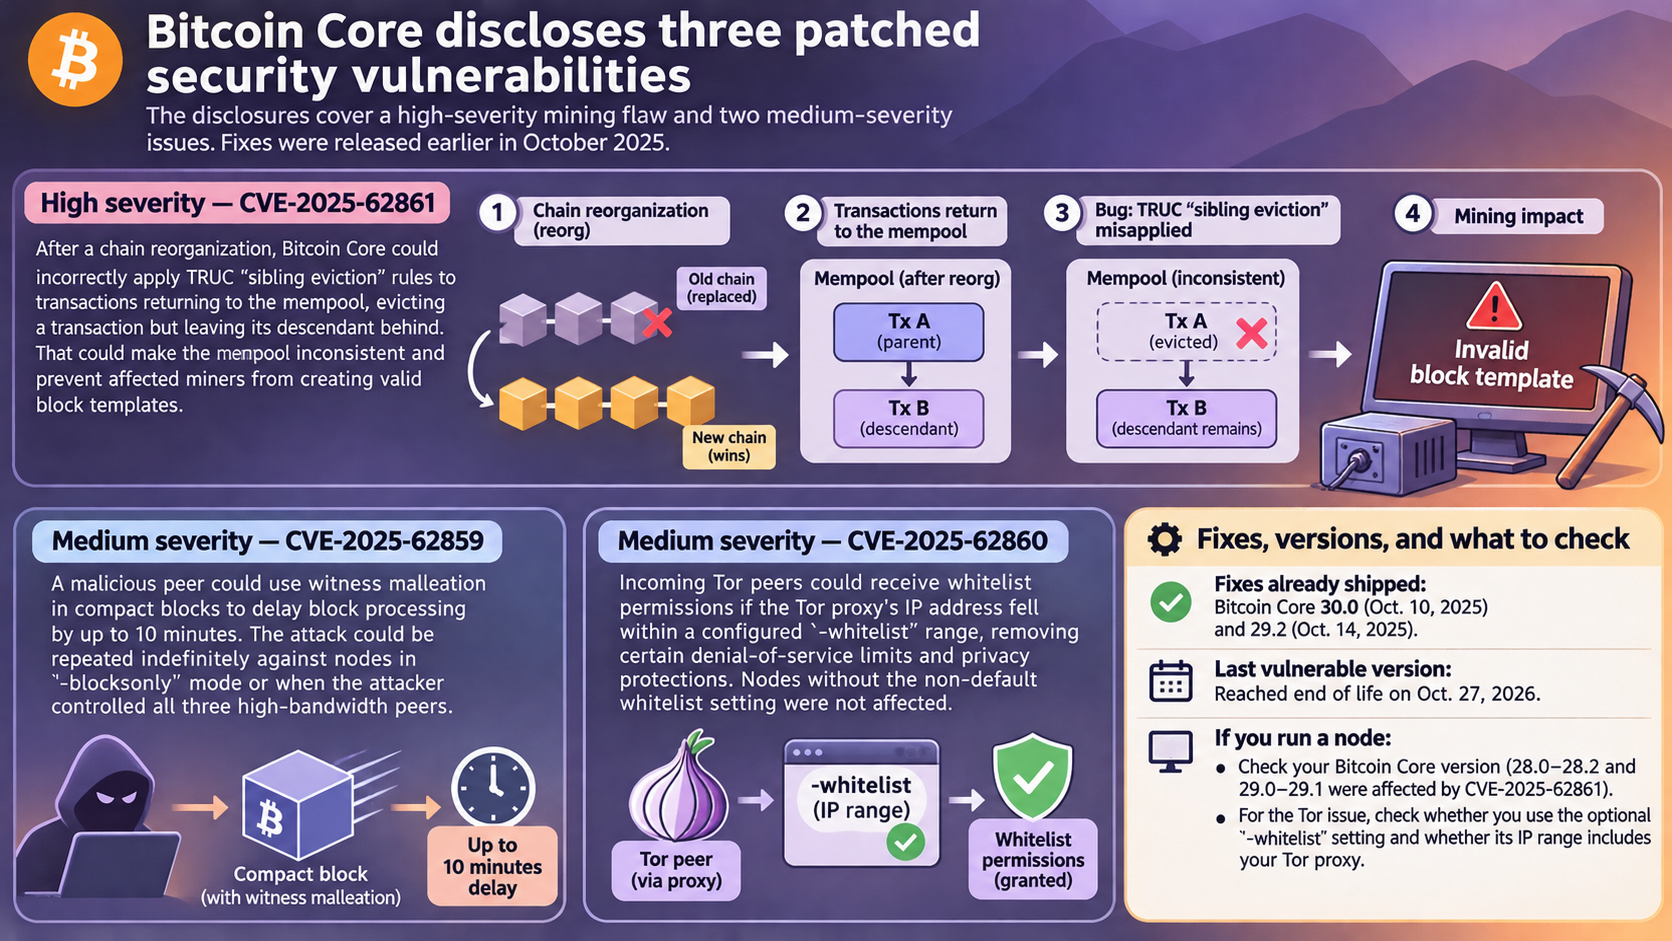
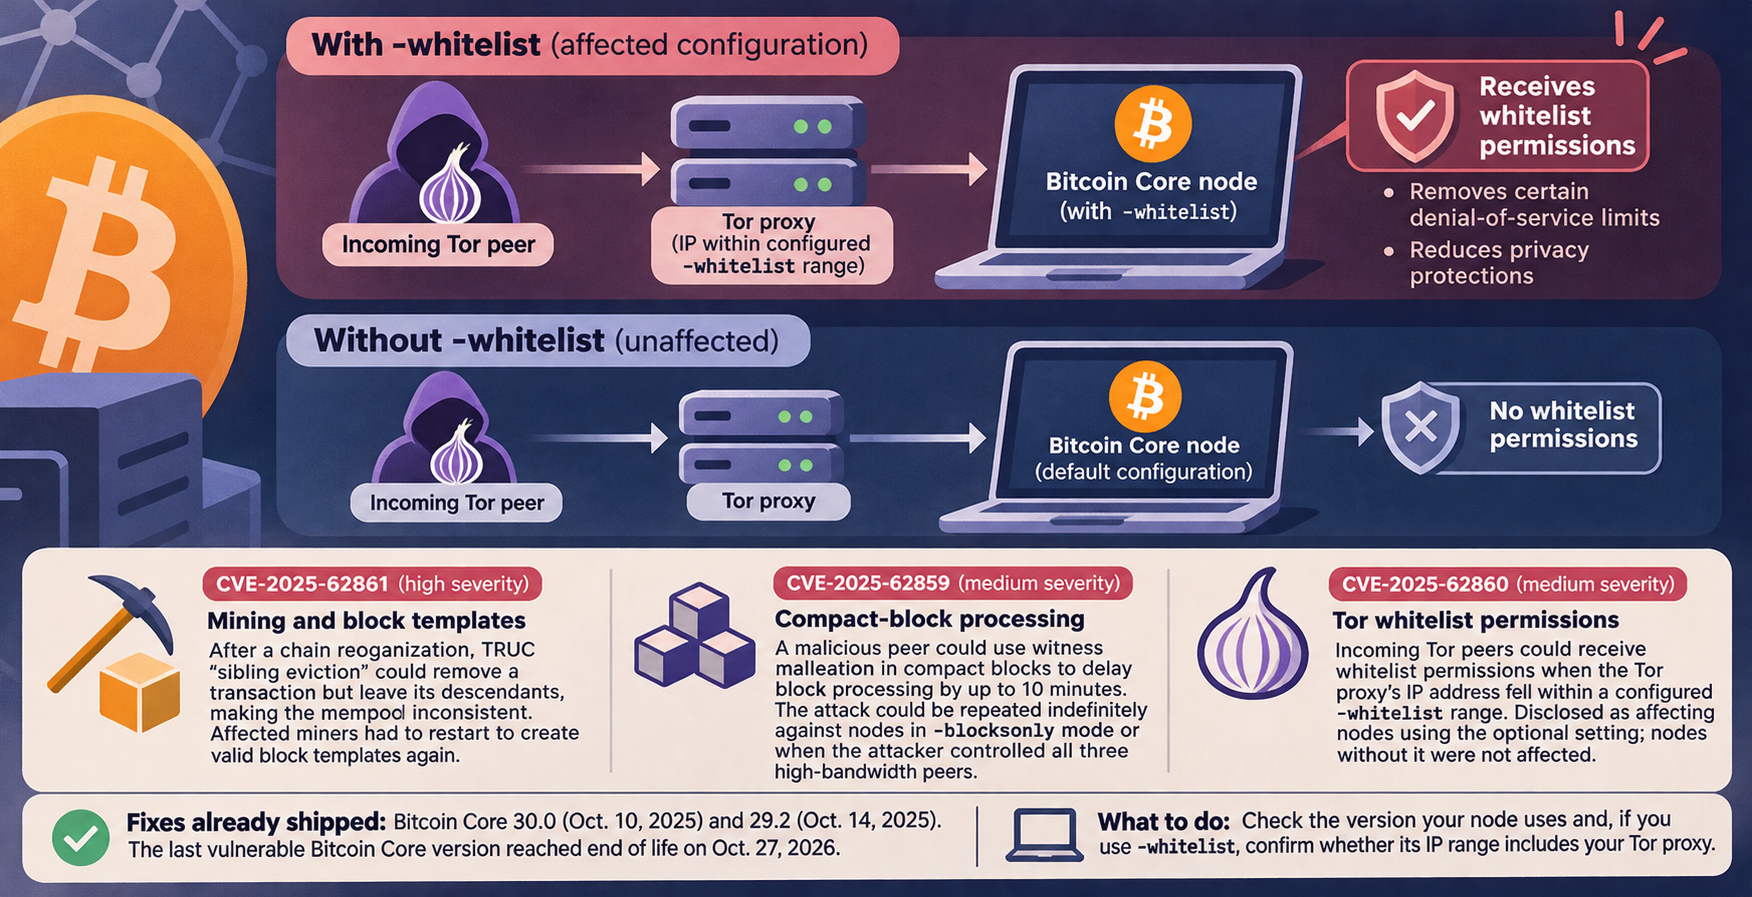
If you run Bitcoin Core, check which version your node uses against the patched releases. The high-severity mining flaw, CVE-2025-62861, affected versions 28.0–28.2 and 29.0–29.1. For the Tor-related flaw, check whether you use the optional -whitelist setting and whether its configured IP range includes your Tor proxy. Nodes without that non-default setting were not affected by the Tor flaw.
What the disclosures describe
- Mining and block templates — high severity: Niklas Goegge reported CVE-2025-62861 on September 26, 2025. After a chain reorganization, Bitcoin Core could incorrectly apply TRUC “sibling eviction” rules to transactions returning to the mempool. That could remove a transaction but leave its descendants behind, making the mempool inconsistent. Affected miners had to restart their nodes before they could create valid block templates again.
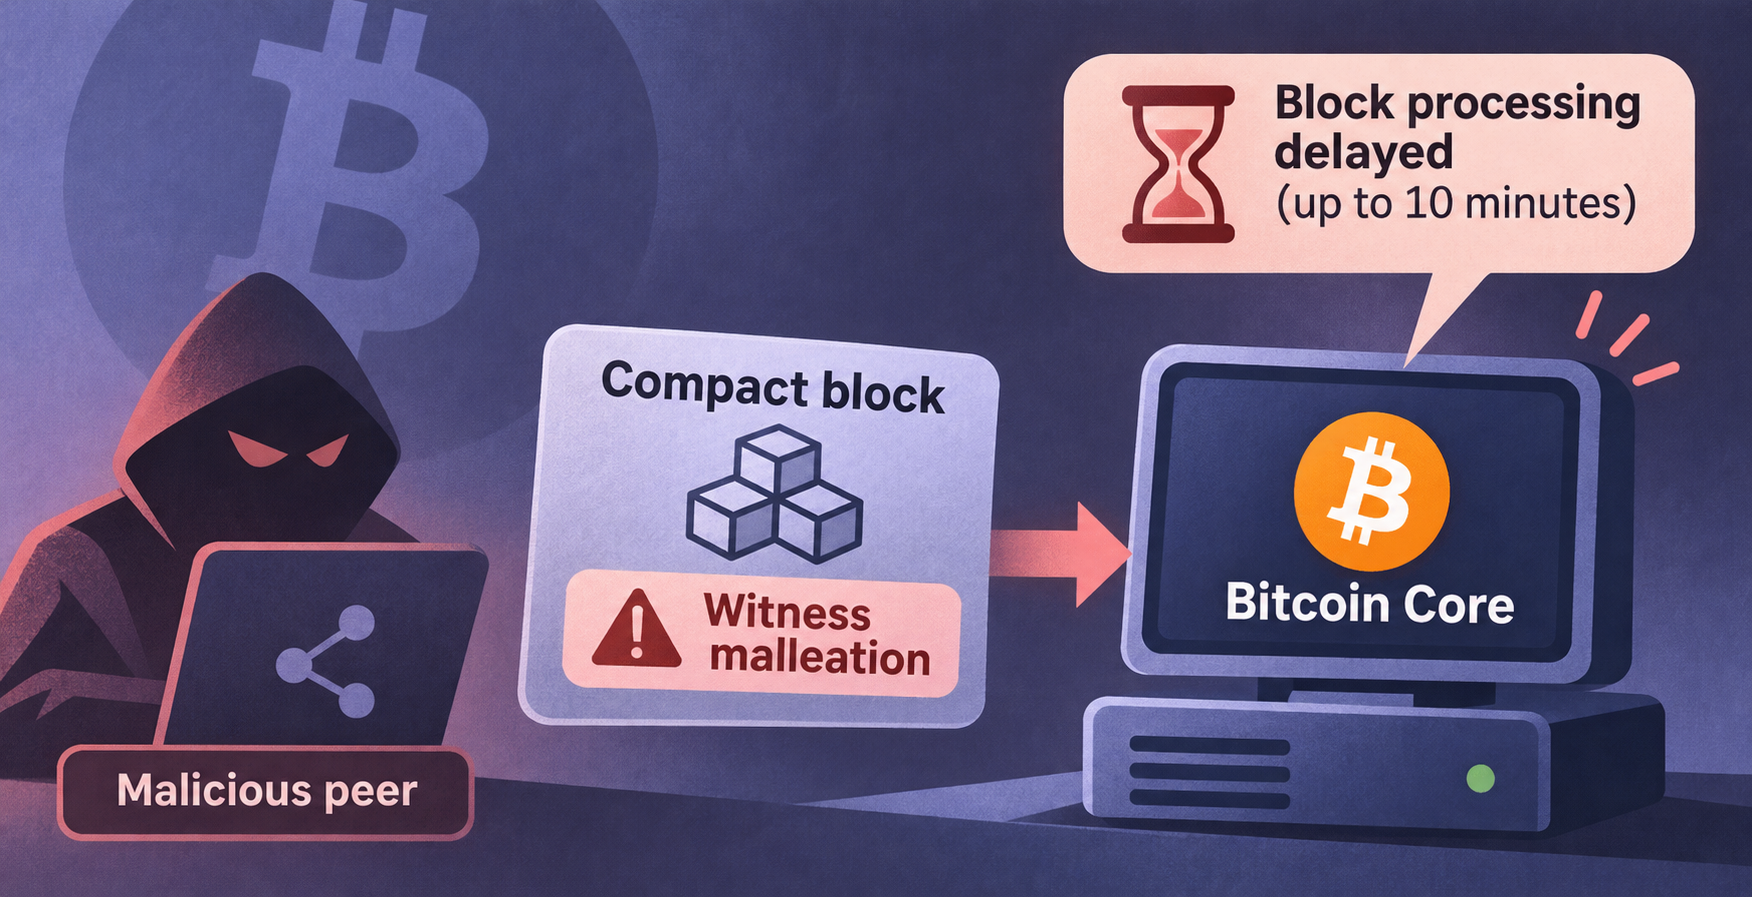
- Compact-block processing — medium severity: Eugene Siegel reported CVE-2025-62859 in April 2025. A malicious peer could use witness malleation in compact blocks to delay block processing by up to 10 minutes. According to the advisory, the attack could be repeated indefinitely against nodes in
-blocksonlymode or when the attacker controlled all three high-bandwidth peers. - Tor whitelist permissions — medium severity: CVE-2025-62860 could give incoming Tor peers whitelist permissions when the Tor proxy’s IP address fell within a configured
-whitelistrange. Bitcoin Core said “thousands” of reachable mainnet nodes had been whitelisting incoming Tor connections, removing certain denial-of-service limits and privacy protections.
According to the advisories, the last vulnerable Bitcoin Core version reached end of life on October 27, 2026. That status is not a substitute for checking the version and configuration of a node you operate.
Source: theblock.co (originally published 2026-11-11 20:49 UTC+8)