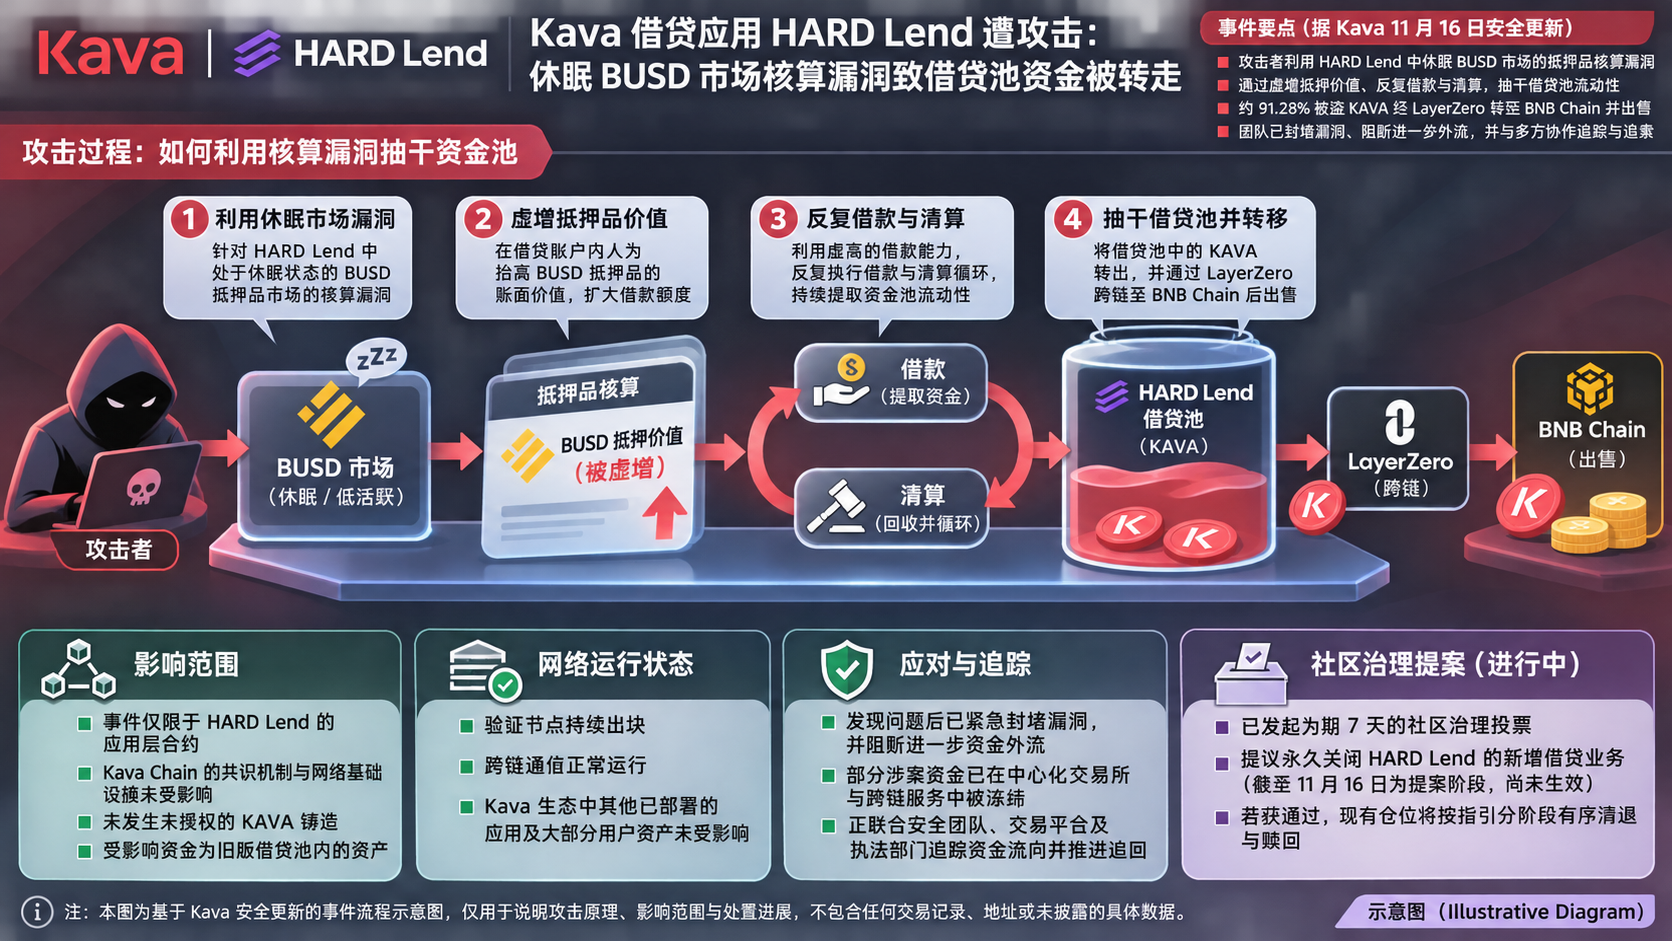
As reported on November 16, 2026, Kava Chain said an attacker had exploited an accounting flaw in HARD Lend, its lending application, and removed approximately 53.9 million KAVA from its lending pools, valued at about $1.83 million.
How the attack worked
According to Kava’s security update, the flaw was in the collateral accounting for a dormant BUSD market. The attacker inflated the recorded value of BUSD collateral in a lending account, then repeatedly borrowed and liquidated positions against the resulting borrowing capacity, draining available pool liquidity.
The report cited on-chain data showing that roughly 49.2 million of the KAVA taken—91.28%—was transferred to BNB Chain through LayerZero and sold. Kava said it had blocked further outflows after identifying the flaw. As of November 16, it said some funds connected to the attack had been frozen at centralized exchanges and bridging services, while contributors worked with security teams, exchanges and law enforcement to trace funds and pursue recovery.
What the proposed shutdown means
Kava said the incident was confined to HARD Lend’s application-layer contracts: its chain’s consensus and network infrastructure were not compromised, and no unauthorized KAVA was minted. It said the affected funds were in the legacy lending pools, while validators and cross-chain communication continued operating.
Kava also opened a seven-day community governance vote on permanently closing HARD Lend to new lending activity. That closure was a proposal, not an enacted rule at the time of the report. If approved, existing positions would be wound down in stages under redemption guidance.